
Research
Model research
We study how a model keeps an accurate picture of changing infrastructure, reasons about what an attacker may be trying to do, and acts only within explicit policy, with the evidence behind each decision kept on record.
The questions that guide the work
Live infrastructure state
How can a model maintain a useful account of an environment that changes while it is being observed?
Attacker intent
What evidence separates an attack path from an unusual but legitimate change?
Cross-domain reasoning
How should evidence from different infrastructure domains change the same threat hypothesis?
Uncertainty
How should the system behave when evidence is incomplete, contradictory, or late?
Policy boundaries
Can authority be represented clearly enough to govern a response while an incident is unfolding?
Controlled response
What is the smallest defensible action that can interrupt an attack path?
Evidence preservation
Can another person reconstruct why the system reached a conclusion and what followed?
Evaluation
How do we test reasoning quality when the safest answer may be to wait, escalate, or refuse an action?
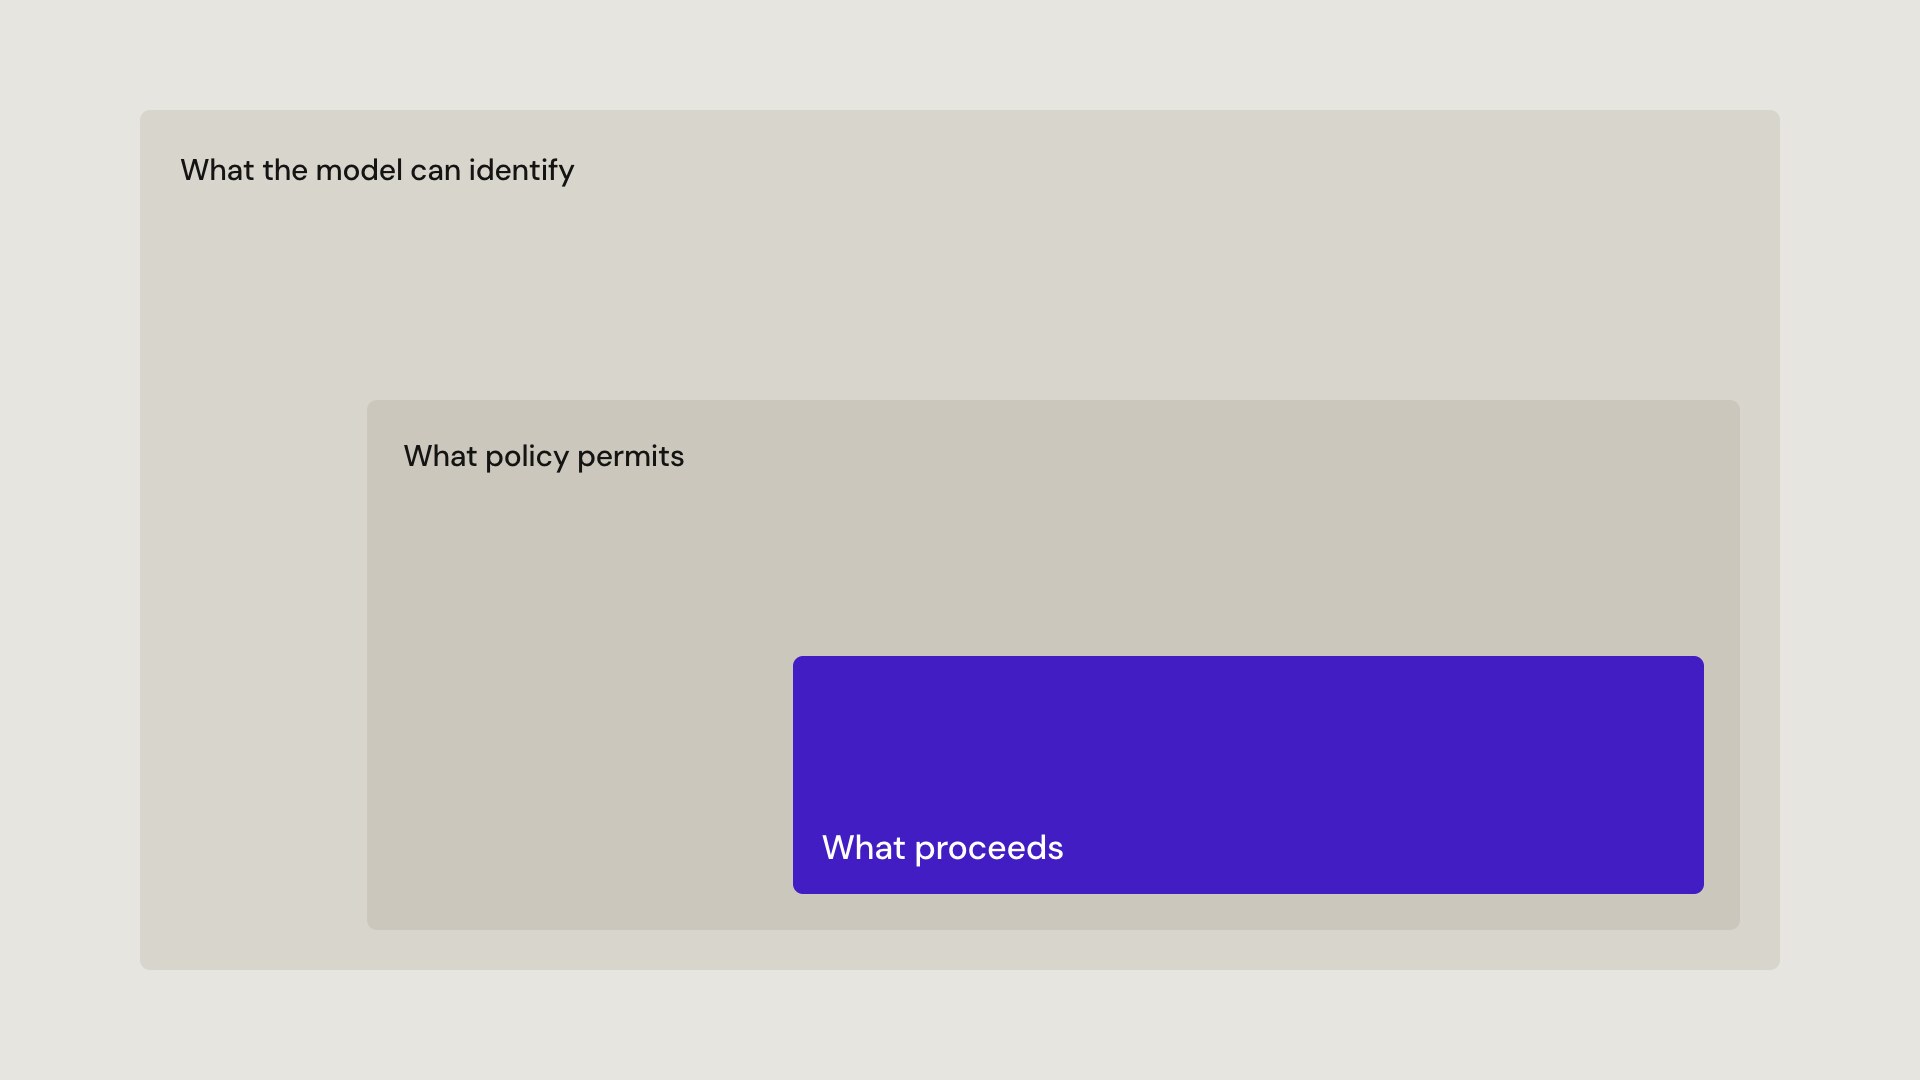
Capability does not grant authority
A model can identify a plausible response without being permitted to carry it out. Policy decides what can be proposed, what needs approval, what can proceed and when the system must stop, and that check is part of the reasoning record.
From observation to review
State
What is happening across the environment now?
Intent
Which explanation best accounts for the evidence?
Authority
What is permitted under current policy?
Response
What controlled action is proportionate?
Evidence
What must remain available for review?