
Glemad Research
The science of intelligence that can be trusted to defend the systems the world depends on.
Research record. Programme of Glemad Research · Research directions: Threat Detection & Incident Interpretation; Autonomous Defense; Safety-Critical Reasoning; Infrastructure Stability & System Behavior; Scalable Compliance Understanding · Governed by the Glemad Safety Framework · Every publication listed in the Research Index
Purpose
Glemad Research builds the science behind intelligence that defends critical systems without becoming a new source of risk. Payments, networks, power, public services, hospitals and the data centres that carry them now depend on software that changes faster than people can follow. Defending them will increasingly fall to systems that reason in real time and act where people cannot reach in time.
Our work is to make those systems correct, bounded and accountable. A defensive system has to keep an accurate picture of an environment that never stops changing, understand what an adversary is trying to achieve, act only within the authority people grant it, and leave evidence that another person can examine and challenge. Each of these is a research problem before it is an engineering one, and each becomes harder as systems become more capable.
Research directions
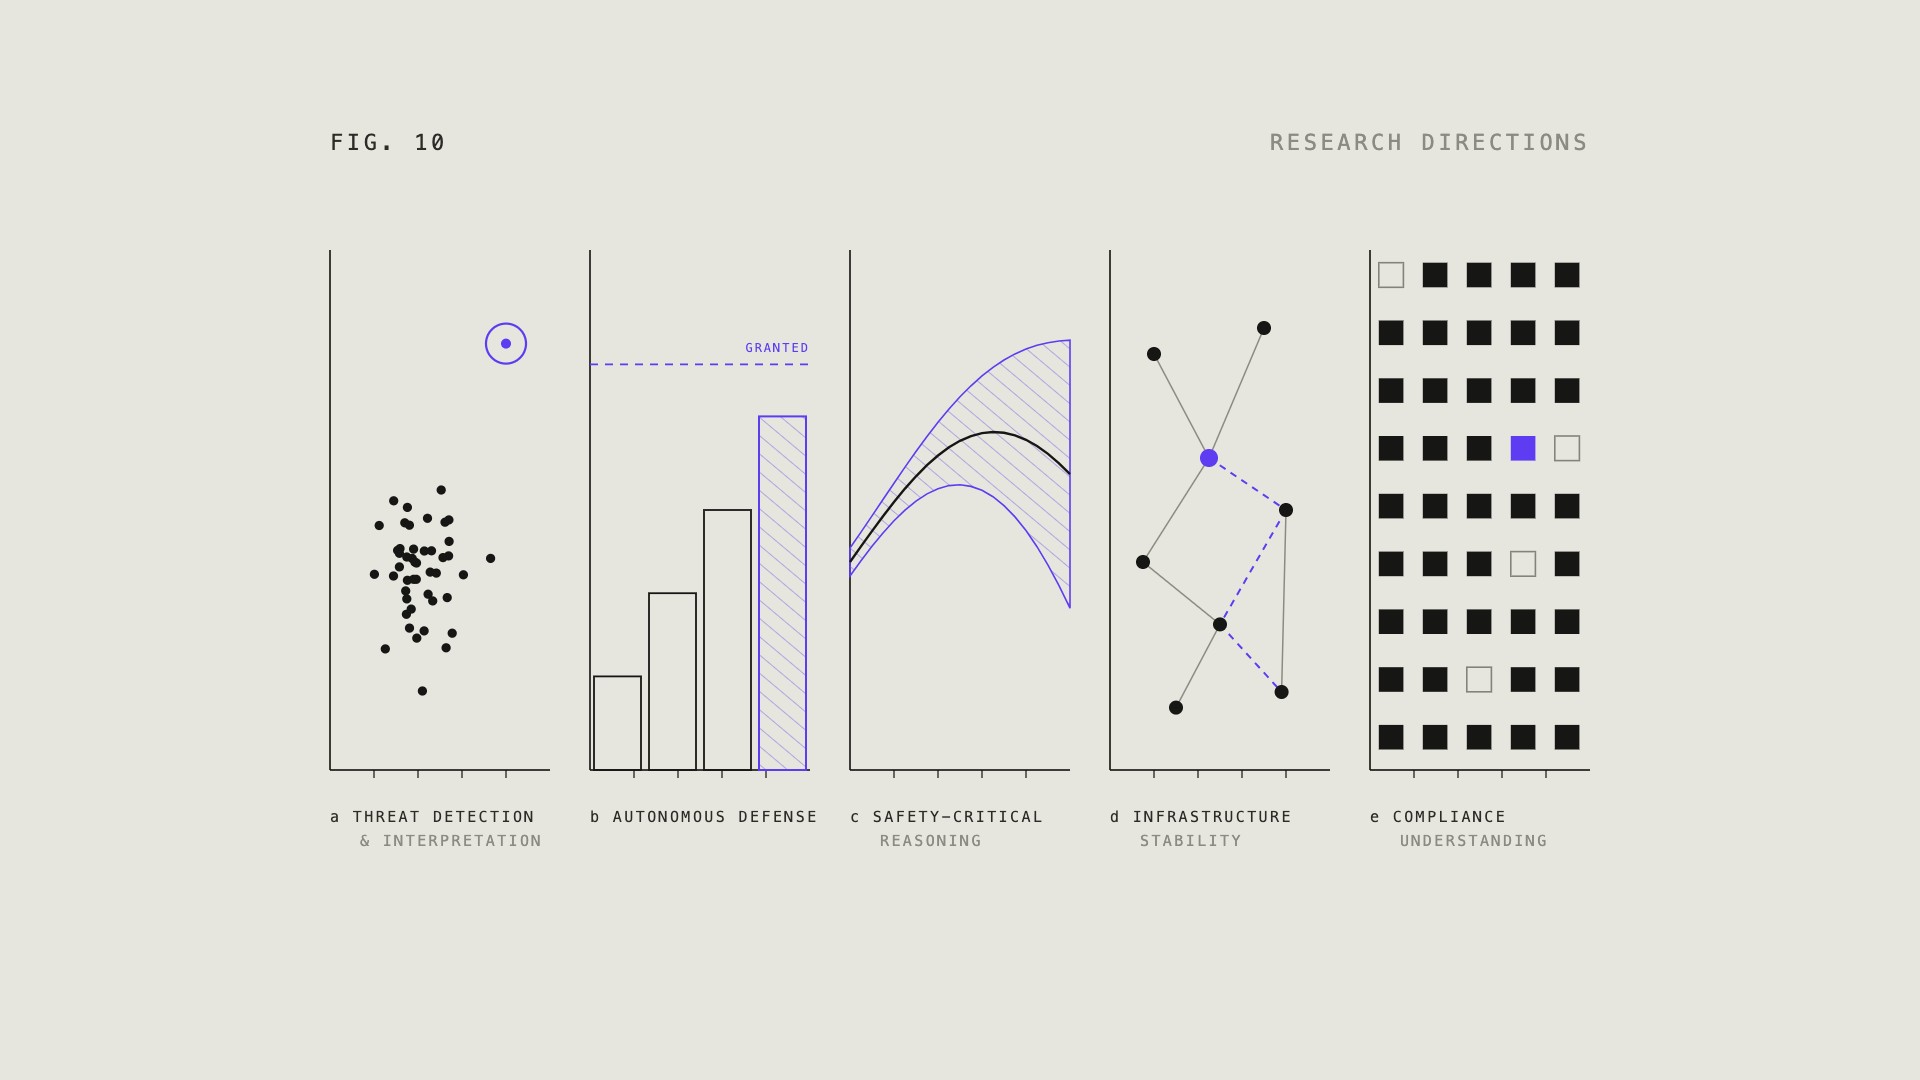
1. Threat Detection & Incident Interpretation
How intelligence identifies emerging risk, correlates signals across an environment and interprets complex events while they are still small.
- Log reasoning
- Anomaly detection
- Triage and prioritisation
- Attack pattern recognition
- System-wide incident interpretation
2. Autonomous Defense
How a system takes controlled defensive action based on verified reasoning, within the authority an institution grants it.
- Policy-bounded response
- Containment strategies
- Behaviour simulation
- Decision-responsibility frameworks
3. Safety-Critical Reasoning
How intelligence stays stable when evidence is incomplete, conflicting or adversarial.
- Reliability in high-pressure environments
- Reasoning under uncertainty
- Robustness evaluation
- Interpretability of defensive decisions
4. Infrastructure Stability & System Behavior
The patterns, dependencies and dynamics that govern distributed systems, and how disruption travels through them.
- Failure mode analysis
- Cross-service behaviour modelling
- Dependency mapping
- Predicting cascading disruptions
5. Scalable Compliance Understanding
How intelligence reads regulatory text, maps controls and assesses an institution's posture continuously.
- Control reasoning
- Evidence validation
- Continuous compliance evaluation
- Audit-ready reporting
Current studies
- Policy-centred modelling
- Multi-agent defensive coordination
- Real-time environmental simulation
- Cross-domain reasoning across OT and IT systems
- Formal verification of reasoning processes
- Adversarial world models
Our published papers are available from Reports.
Threat intelligence
Glemad publishes threat intelligence and institutional guidance drawn from the environments our systems defend. The Glemad African Threat Intelligence Report (GATIR) assesses the threat environment across Africa’s financial infrastructure, telecom networks, government systems and critical digital services, built on direct telemetry, regulatory disclosures and law enforcement reporting. Our regulatory guidance translates new obligations, such as the Central Bank of Nigeria's data localisation mandate, into infrastructure security practice.
Evaluation
Every model and every capability is evaluated before it is given authority, and evaluation continues after release. We test reasoning integrity, calibration of uncertainty, adherence to authority boundaries, the consequence of each proposed response, and whether a decision can be reviewed by a person who was not there. Red-teaming is internal, independent and institutional. The standard is set out in full in the Model Evaluation and Red-Teaming Standard.
Safety
All Glemad research is governed by the Glemad Safety Framework. Authority is granted by people and never learned. An irreversible action requires a person. Every action is reversible by design or it is held. Everything is recorded, including what was considered and rejected. The more capable a system becomes, the more it must demonstrate before it may act, and the more of the framework applies to it.
From research to practice
Research reaches institutions through Ollandi, Glemad's continuous defence platform, under the level of authority each institution grants: Observe & Notify, Assisted Response or Controlled Autonomy. What a system may do at each level is defined in the Safe Autonomy Framework, and how it is introduced into a new environment is defined in the Responsible Deployment Framework.
How we publish
We publish methods, findings and the conditions under which they hold, so that the institutions affected by our work can examine it. Every publication carries its date and revision history and is listed in the Research Index. Papers, threat intelligence and guidance are available from Reports.
Research with us
The Young Researchers Fellowship gives early-career researchers protected time to take one question in AI security to a finished, reviewable piece of work. Researchers and engineers who want to work on these questions full time can find open roles through Careers at Glemad.