
Safe Autonomy Framework
The permanent boundaries of autonomous action by any Glemad system: what it does alone, what it asks, and what always rests with a person.
Framework record. Version 2.0 · Effective 14 November 2026 · Supersedes version 1.0 (2025) · Owner: Glemad Research, with Security Engineering · Reviewed with the Glemad Safety Framework
Purpose
A system that acts in production could become the outage, or could be turned against the environment it protects. This framework answers that risk with mechanisms, each specified in Glemad's published research and enforced in every system it ships. The framework is written for systems that will reason faster than people can follow and act in places people cannot reach in time. The faster and more capable the system, the more tightly these rules bind it.
Four invariant rules
- Authority is granted, never learned. People write policy. The policy boundary sits outside every learned component. Learning improves judgement; it cannot extend permission.
- Irreversible actions require a person. Whatever the confidence, whatever the consensus, whatever the speed.
- An action is reversible by design, or it is held. Reversible actions keep a pre-action snapshot, a rollback procedure and verification criteria.
- Everything is recorded, including what was rejected. Observations, hypotheses, candidate actions, policy checks, dissent, the action and its verified outcome, in tamper-evident form.
These rules are not configurable. No policy, contract, emergency or framework revision below the level of the Glemad Safety Framework can relax them.
Authority tiers
An institution grants authority per scope, in versioned policy:
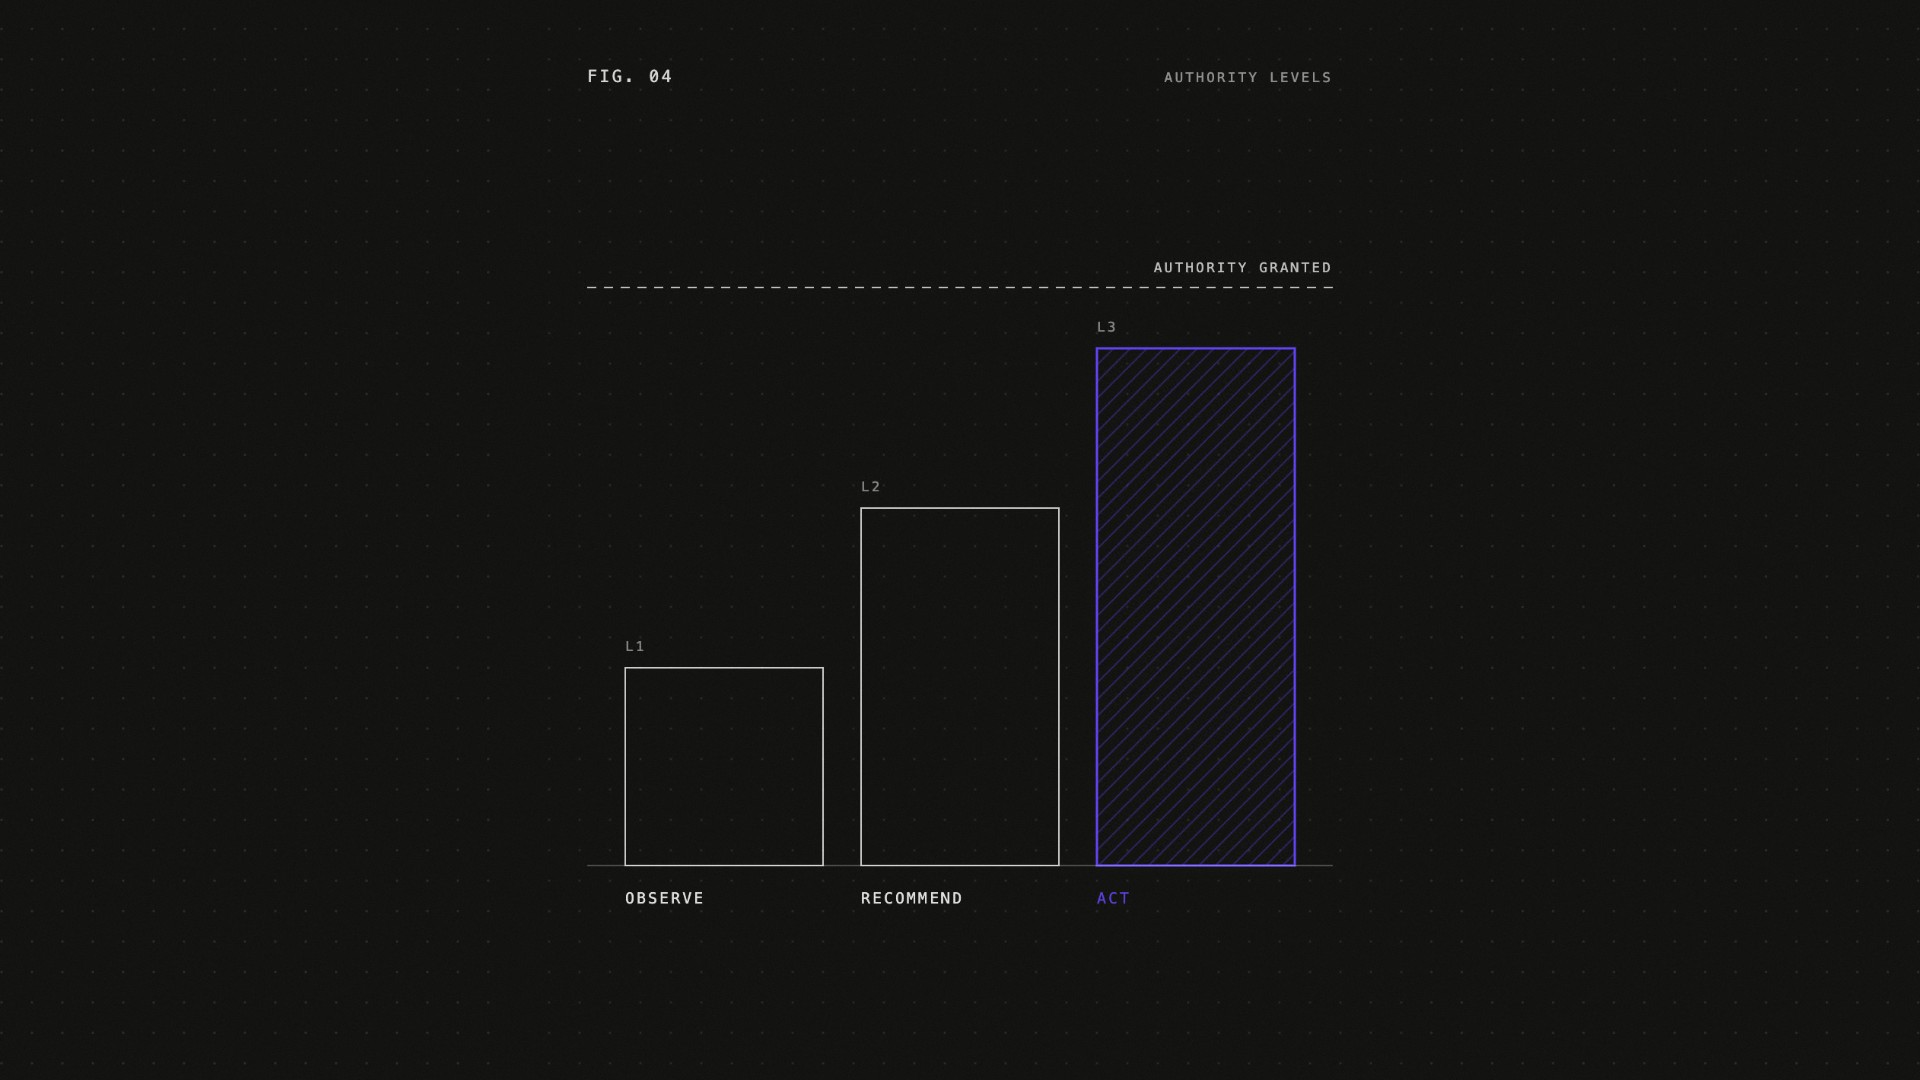
- Observe & Notify. The system watches and explains. The institution makes every change.
- Assisted Response. The system prepares each response with policy and rollback checks. A person signs every action.
- Controlled Autonomy. The system acts at machine speed within the rules the institution set.
Action classes
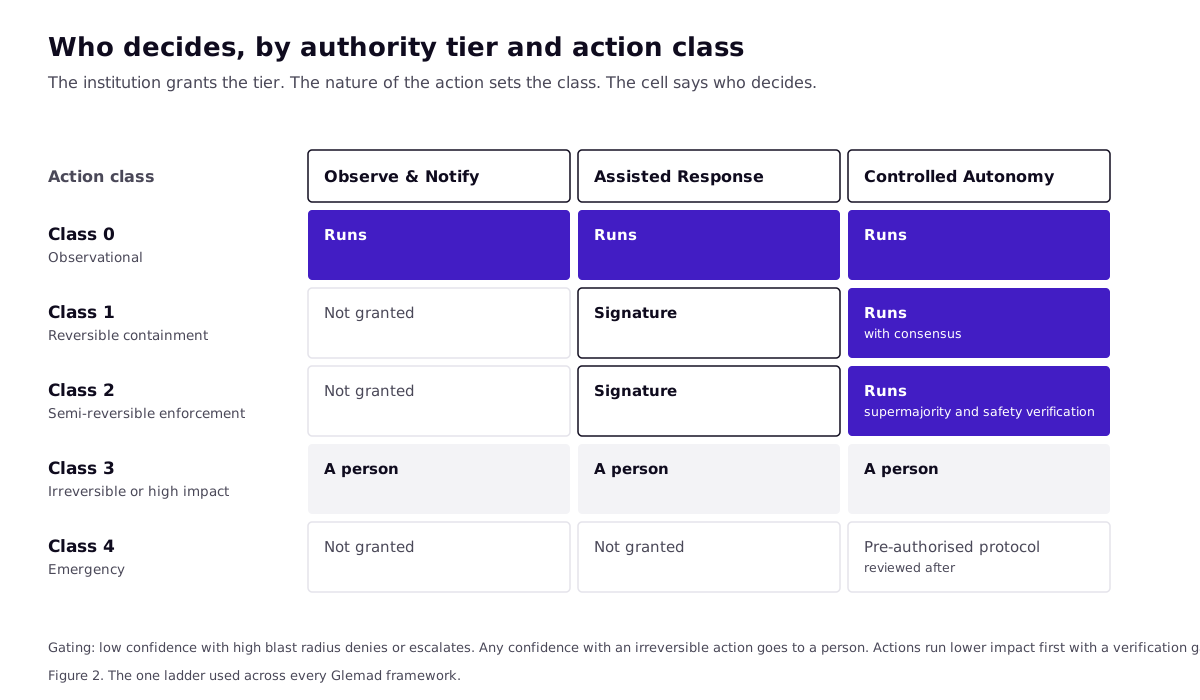
An action's class is a property of the action, graded by reversibility and impact, independent of who proposes it or how confident they are.
Class | Nature | Examples | Decision |
|---|---|---|---|
0 | Observational; no change to infrastructure | Evidence collection, monitoring enhancement, risk-score updates, deception deployment | The system, always |
1 | Reversible containment; temporary restriction with explicit rollback | Session revocation, temporary network block, API throttling, privilege suspension, step-up authentication | The system under Controlled Autonomy, with consensus |
2 | Semi-reversible enforcement; operational impact, recoverable | Credential rotation, workload quarantine, deployment rollback, host isolation, policy parameter lock | The system under Controlled Autonomy, with supermajority consensus and safety verification |
3 | Irreversible or high impact | Resource deletion, account disablement, data destruction, policy rewrite, broad network isolation | A person, always |
4 | Emergency; catastrophic threat requiring immediate broad action | Site-wide containment, mass session termination, emergency segmentation | Pre-authorised protocols only, with mandatory review afterwards |
Gating
Class and authority combine with confidence and blast radius. Low confidence with high blast radius: deny or escalate. Moderate confidence with a reversible action: execute. High confidence with a semi-reversible action: execute with safeguards. Any confidence with an irreversible action: a person decides. Under Observe & Notify nothing above Class 0 runs. Under Assisted Response nothing above Class 0 runs without a signature. Actions are sequenced lower impact first, with a verification gate between steps and escalation on verification failure.
The checks before any action
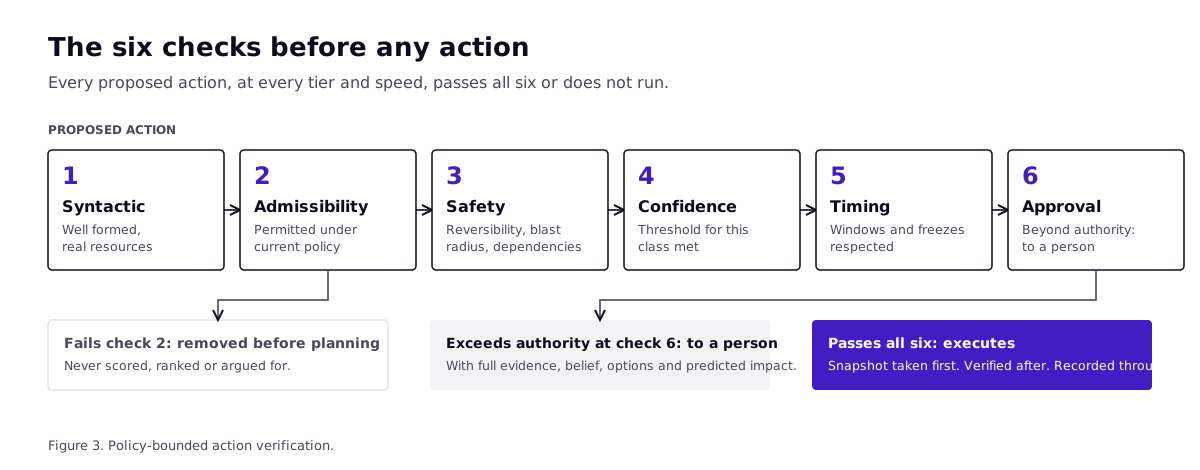
Every proposed action, at every tier and speed, passes six checks:
- Syntactic validation. Well formed; references resources that exist.
- Policy admissibility. Permitted for this agent on this resource under current policy.
- Safety constraints. Reversibility, blast radius, dependencies and operational impact within limits.
- Confidence threshold. Met for this action class.
- Temporal constraints. Permitted now, given maintenance windows and change freezes.
- Approval routing. Anything beyond autonomous authority goes to the right human role with full evidence.
A candidate that fails policy admissibility is removed before planning. It is not scored, ranked or argued for.
Collective decisions
Where specialised agents decide together, the consensus requirement rises with impact. Class 1 requires a simple majority of relevant domain agents. Class 2 requires a supermajority including at least one agent from outside the domain. Class 3 requires a person regardless of agreement. No single agent can determine a collective decision. Dissent is recorded and escalated, never overridden. An agent whose behaviour deviates is excluded until examined. Under partition, agents holding quorum continue with reduced confidence and expanded evidence capture; agents that have lost quorum escalate to people.
Human command points
Human review is mandatory when policy requires it; when the action is irreversible; when predicted operational impact exceeds the institution's threshold; when uncertainty is high or candidate futures cannot be told apart; when the observation channel is suspected to be compromised; when agents disagree beyond permitted variance or consensus has not formed within its time bound; and when inputs are ambiguous or signals conflict.
The person receives the current belief, competing hypotheses, candidate actions, predicted consequences, uncertainty, policy checks and predicted operational impact. Authorised people may override any autonomous decision at any time. The override and its reason are recorded.
Doing less
Doing less is a legitimate decision and the framework is built to permit it. When every containment option carries unacceptable uncertainty or tail risk, the system may act to learn: step-up authentication, targeted trace capture, a decoy, a temporary narrowing of privilege, or a reversible action whose outcome separates competing hypotheses. Planning is receding-horizon: the system executes only the first authorised action, observes, updates its belief and plans again. It never commits to a multi-step plan it has not re-checked against reality. High-impact actions receive shorter horizons and stricter uncertainty bounds.
Reversibility and rollback
Class 1 and Class 2 actions keep a pre-action snapshot, a rollback procedure and verification criteria. Rollback is triggered by unintended disruption, a drop in confidence, a human override or a detected policy violation. Across domains, rollback respects causal order. Every rollback is recorded.
Emergencies
Class 4 exists for the case where waiting is the catastrophe. It runs only under protocols the institution authorised in advance, naming trigger, scope, bounded worst-case impact and the review that must follow. Emergency responders cannot authorise their own emergency actions. Every Class 4 action is reviewed afterwards with the full record, and a protocol found to have acted outside its scope is suspended.
Limits on learning
A Glemad system learns from confirmed threats, false positives, missed threats, human feedback and environmental change, under four hard constraints: authority bounds cannot expand; hard safety rules are invariant; the rate of parameter change is capped; and every update is logged with before and after values, triggering signals and approval status. Model parameters change only through governed offline training, evaluation, shadow operation and promotion, never through a live loop. The system may propose an action beyond its boundary. It cannot move the boundary.
Separation of duties
- Policy authors cannot approve their own policy changes.
- System operators cannot modify an agent's authority bounds.
- Analysts reviewing an incident cannot modify the policies that governed it.
- Emergency responders cannot authorise their own emergency actions.
Guarantees of conduct
Every Glemad system, at every tier and in every deployment, acts only inside a recorded policy boundary, leaves its own authority, safety thresholds and policy to the people who own them, refers every irreversible action to a person, acts openly within the institutions it serves, and preserves every record of its own decisions intact. These guarantees are enforced by construction and tested at every release.
Validation
Before authority is granted, autonomous behaviour is tested in simulated environments, failure scenarios, low-visibility conditions and adversarial contexts, then run in shadow against the real environment. After it is granted, the system is monitored for drift, degradation and boundary breaches. Policy violations, irreversible actions without approval and blast-radius exceedances carry a target of zero and are reported to the institution. If stated uncertainty stops predicting error, autonomy is withdrawn and the system returns to advisory operation.
Raising the ceiling
The ceiling on autonomy set here, with Class 3 always a person's decision, is a position Glemad holds deliberately. Should Glemad ever propose to change it, the proposal will require a revision of the Glemad Safety Framework, a published rationale, evaluation at the relevant tier, independent review, and the recorded agreement of the institutions affected. Until then, no system Glemad builds, however capable, will decide an irreversible action alone.