
Compliance and Governance
The record every decision leaves, who may change the rules, how Glemad governs itself, and how an auditor, a regulator or a board can verify all three.
Framework record. Version 2.0 · Effective 14 November 2026 · Supersedes version 1.0 (2025) · Owner: Glemad Policy, with the Office of the CEO · Reviewed with the Glemad Safety Framework
Principle
Compliance requirements are constraints on how systems behave. Encryption, least privilege, approved network paths and change control must hold every day, including the days no auditor is looking. Documentation cannot satisfy a runtime requirement. A Glemad system treats compliance as a reasoning problem: infer whether the current state satisfies the constraint, produce evidence at the moment of decision, and ensure any remediation is safe, authorised and recorded. The same standard governs Glemad itself.
Governance principles
- Policy alignment. The system operates inside the policies that define acceptable behaviour, access rights and escalation paths. It enforces them and does not define them.
- Traceable authority. Every permission the system holds traces to a named owner and an approved, versioned policy.
- Evidence by default. Evidence is produced as part of the decision, never reconstructed afterwards.
- Separation of duties. No single role both sets the rules and acts under them.
- Accountability stays with people. With the institution that grants authority, and with Glemad as designer, for as long as the system runs.
The evidence standard
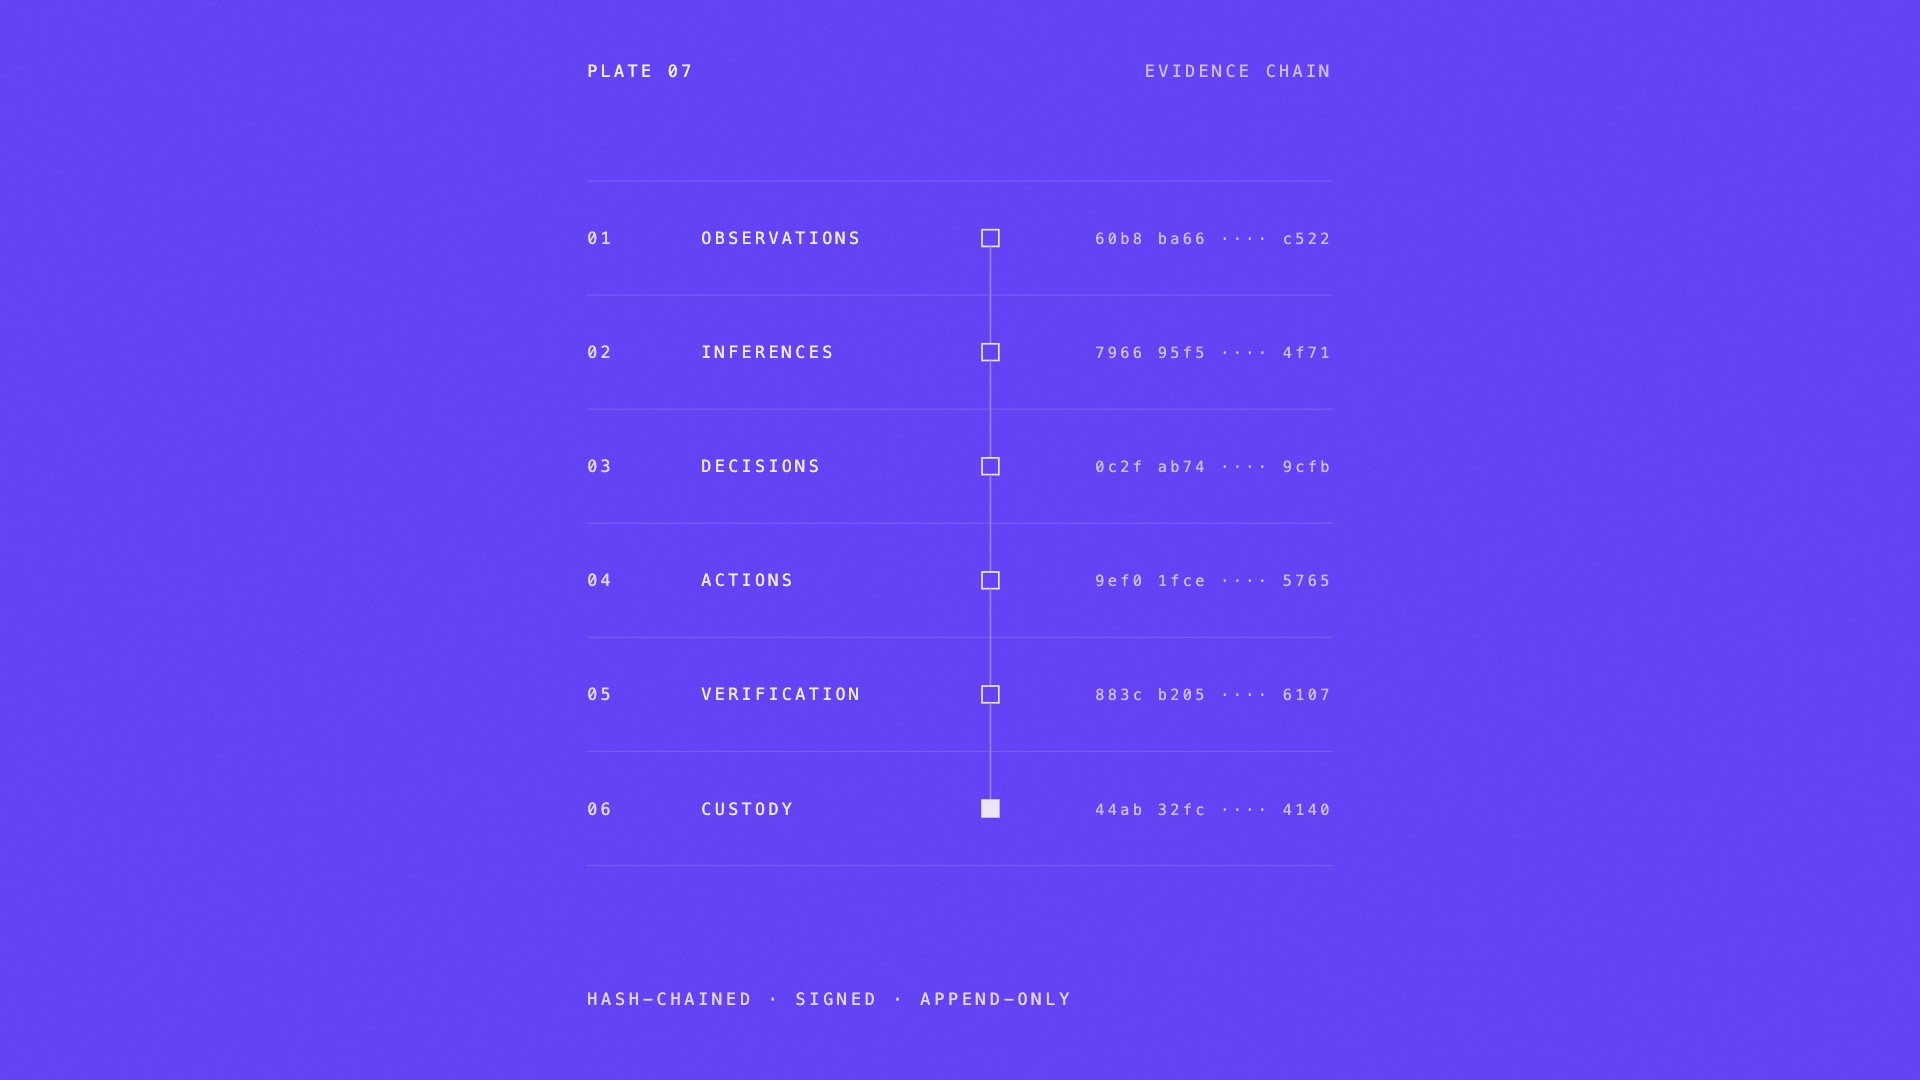
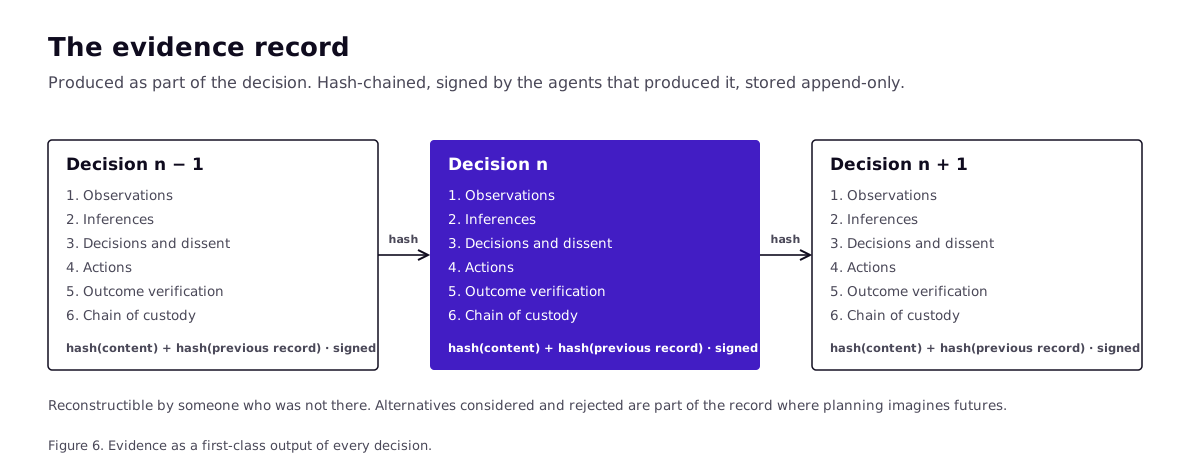
Every significant decision produces an evidence bundle of six parts: observations with provenance, timestamps and integrity verification; inferences with hypotheses, confidence, supporting evidence and reasoning chain; decisions with the consensus record, policy checks, thresholds and preserved dissent; actions proposed and executed with validation, timestamps and verification; outcome verification confirming effect or identifying unintended consequence; and chain of custody.
Each record carries a hash of its content and of the previous record. Bundles are signed by the agents that produced them, verifiable against agent identity certificates, and stored append-only with tamper-evident auditing. Where a system plans over alternative futures, the alternatives considered and the reasons for rejecting them are part of the record, so that evidence shows what was weighed as well as what was done.
Two measures are reported to every institution: audit readiness, the time to produce a complete evidence package for a randomly chosen incident; and chain-of-custody integrity, verified at 30, 60 and 90 days and on demand. The evidence record is designed to answer an auditor's question without Glemad's involvement.
Policy as the control surface
Policy is the instrument through which an institution governs a Glemad system. A policy specifies authority scope; permitted and prohibited action classes by resource criticality and confidence; temporal constraints; blast-radius limits; approval, rollback and evidence requirements; and regulatory obligations including data residency, retention and privilege boundaries.
Policies are versioned. A change requires approval by someone other than its author, impact assessment and audit logging. Policy integrity is monitored continuously, so an attempt to relax a constraint or widen authority, by mistake or by an attacker with policy access, is treated as policy poisoning and refused. Policy is enforced at the moment of action by the checks in the Safe Autonomy Framework, never only at configuration time.
Roles and separation of duties
Outputs and recommendations respect the role, privileges and context of the person receiving them. In every deployment: policy authors cannot approve their own changes; operators cannot modify agent authority bounds; analysts reviewing an incident cannot modify the policies that governed it; emergency responders cannot authorise their own emergency actions. Authorised people may override any autonomous decision; the override, the person and the reason are recorded.
Continuous compliance
The system maps organisational controls to live behaviour and keeps the mapping current as infrastructure changes. It watches for drift between declared policy and real operation and surfaces misconfigurations, violations and control gaps early, with evidence suitable for internal audit, regulatory review and certification, while there is still time to close the gap rather than report it. Remediation is governed by the same action classes as any defence: restoring a drifted encryption setting carries operational impact and is a Class 2 action, taken under Controlled Autonomy only with stronger verification or prepared for signature under Assisted Response.
Regulatory and data boundaries
Data sovereignty, logging and retention rules, privilege boundaries and legal exposure limits are written into policy and enforced like any other constraint. Deployment topologies support regional and on-premises tiers so that where a regulator requires data to remain within a jurisdiction, the deployment is designed to keep it there. Glemad publishes its analysis of regulatory change affecting the infrastructure it protects, including the Central Bank of Nigeria's data localisation mandate effective January 2027.
Governance of Glemad
The discipline Glemad asks of institutions it applies to itself.
Release. A capability leaves research only after evaluation at its tier under the Model Evaluation and Red-Teaming Standard, a published scope statement, shadow operation against the target environment, and a Safety Review. The CEO is the responsible executive.
The Safety Review. The Safety Review is the decision point for every release and for every promotion of a deployment to Controlled Autonomy. It is held by the leads of research, engineering, security and policy, each of whom signs. It receives the evaluation report for the capability's tier, the scope statement, the shadow-mode record, the safety counts, the evidence-completeness scores and the threat-model findings still open. It issues one of three decisions, recorded with its reasons: release, release with named conditions, or hold. A hold cannot be overruled by a commercial decision. The record of each review is kept with the release it concerns.
Change. Model updates follow staged rollout with the safety regression suite and rollback. Policy templates follow the same approval and versioning rules as customer policy. Every reported research result carries a manifest sufficient to reconstruct it.
Research with dual-use potential. Methods and defensive results are published in full. Operational detail that would materially assist an attacker is withheld, and the decision to withhold is recorded and reviewed.
Deviation. A material deviation from any framework is recorded, reported to the responsible executive and communicated to affected institutions with the corrective action taken.
Incident communication
Glemad communicates safety-relevant findings in its systems to affected institutions, with the scope, the mitigation and the fix. Significant events in a deployment are reviewed with the institution and the findings fed back under governance. Published statements are kept current across every document they reach, and each revision is noted.
External review
Glemad submits its methods and positions to scrutiny outside the company: research published with reproduction manifests; independent red-teaming under the Model Evaluation and Red-Teaming Standard; joint testing with institutions that run its systems; and cooperation with auditors and regulators.
Revision
This framework is reviewed with the Glemad Safety Framework on every major model release and at least annually, and whenever regulation, an incident or an external finding shows it to be incomplete. Each revision records what changed and why. Earlier versions remain available.