
Responsible Deployment Framework
How a Glemad system enters a live environment: in stages, with authority earned by evidence, bounded by policy, and withdrawn when the evidence changes.
Framework record. Version 2.0 · Effective 14 November 2026 · Supersedes version 1.0 (2025) · Owner: Glemad Engineering, with Policy · Reviewed with the Glemad Safety Framework
Principle
Every deployment decision begins with the harm a wrong action could cause in that environment, not with what the system can do. A capability that has passed evaluation in general still enters a new environment at the lowest stage, because the environment is what it has not seen. Capability earns authority through evaluation, scope by scope, and the institution grants it in writing.
Applicability
This framework applies to every way a Glemad system reaches a live environment: the Ollandi platform, the Ollandi API, Inline hardware in the network path, systems operated by partners on Glemad technology, and deployments at national or multi-institution scale. The authority tiers and action classes are those of the Safe Autonomy Framework.
Readiness
Before a system runs at any stage, four things are established and recorded.
Policy, written down. The institution's rules encoded as formal constraints: authority scope; permitted, restricted and prohibited action classes by resource criticality and confidence; maintenance windows and change freezes; blast-radius limits; approval requirements; rollback requirements; evidence requirements; and regulatory obligations including data residency and retention. The system enforces this policy. It does not define it.
Roles. The named policy owner; who approves high-impact actions; who may override; who reviews. Separation of duties applies from the first day.
The environment, mapped. Infrastructure, identities, dependencies and recovery paths, and where the institution maintains one, the services and mission objectives those assets support, with risk tiers per asset class.
Observability. Glemad establishes the telemetry coverage each stage requires, records it, and works with the institution to reach it.
Stages of deployment
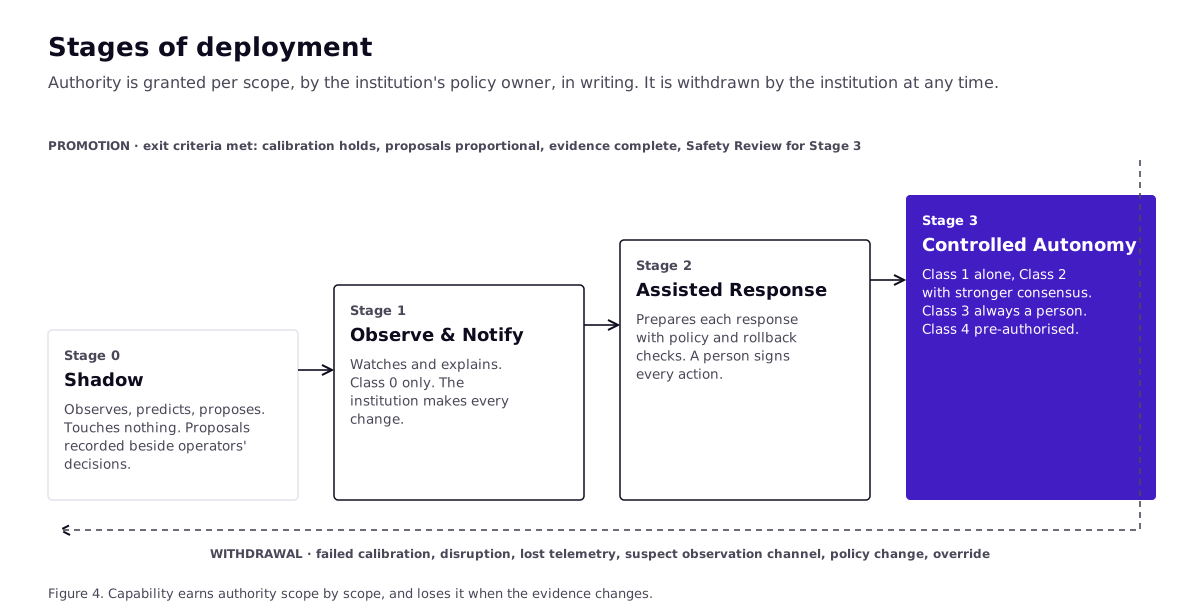
Stage 0: Shadow. The system observes, predicts, ranks and proposes, and touches nothing. Proposals are recorded beside the operators' actual decisions. Exit requires that stated uncertainty predicts error, that proposals are proportional, and that evidence bundles score complete.
Stage 1: Observe & Notify. The system watches and explains; the institution makes every change. Only Class 0 actions run. This is a permanent operating level for institutions that want continuous reasoning without automated change, and it is where every deployment begins its live operation.
Stage 2: Assisted Response. The system prepares each response with policy and rollback checks already run; a person signs. Every action is confirmed by someone who receives the reasoning, confidence, evidence and predicted impact. The person's decision is recorded and informs the evaluation of the next stage.
Stage 3: Controlled Autonomy. Within policy, the system takes Class 1 reversible actions on its own and Class 2 actions under stronger consensus and safety verification. Class 3 actions always require a person. Class 4 emergency actions run only under protocols the institution pre-authorised, with mandatory review afterwards.
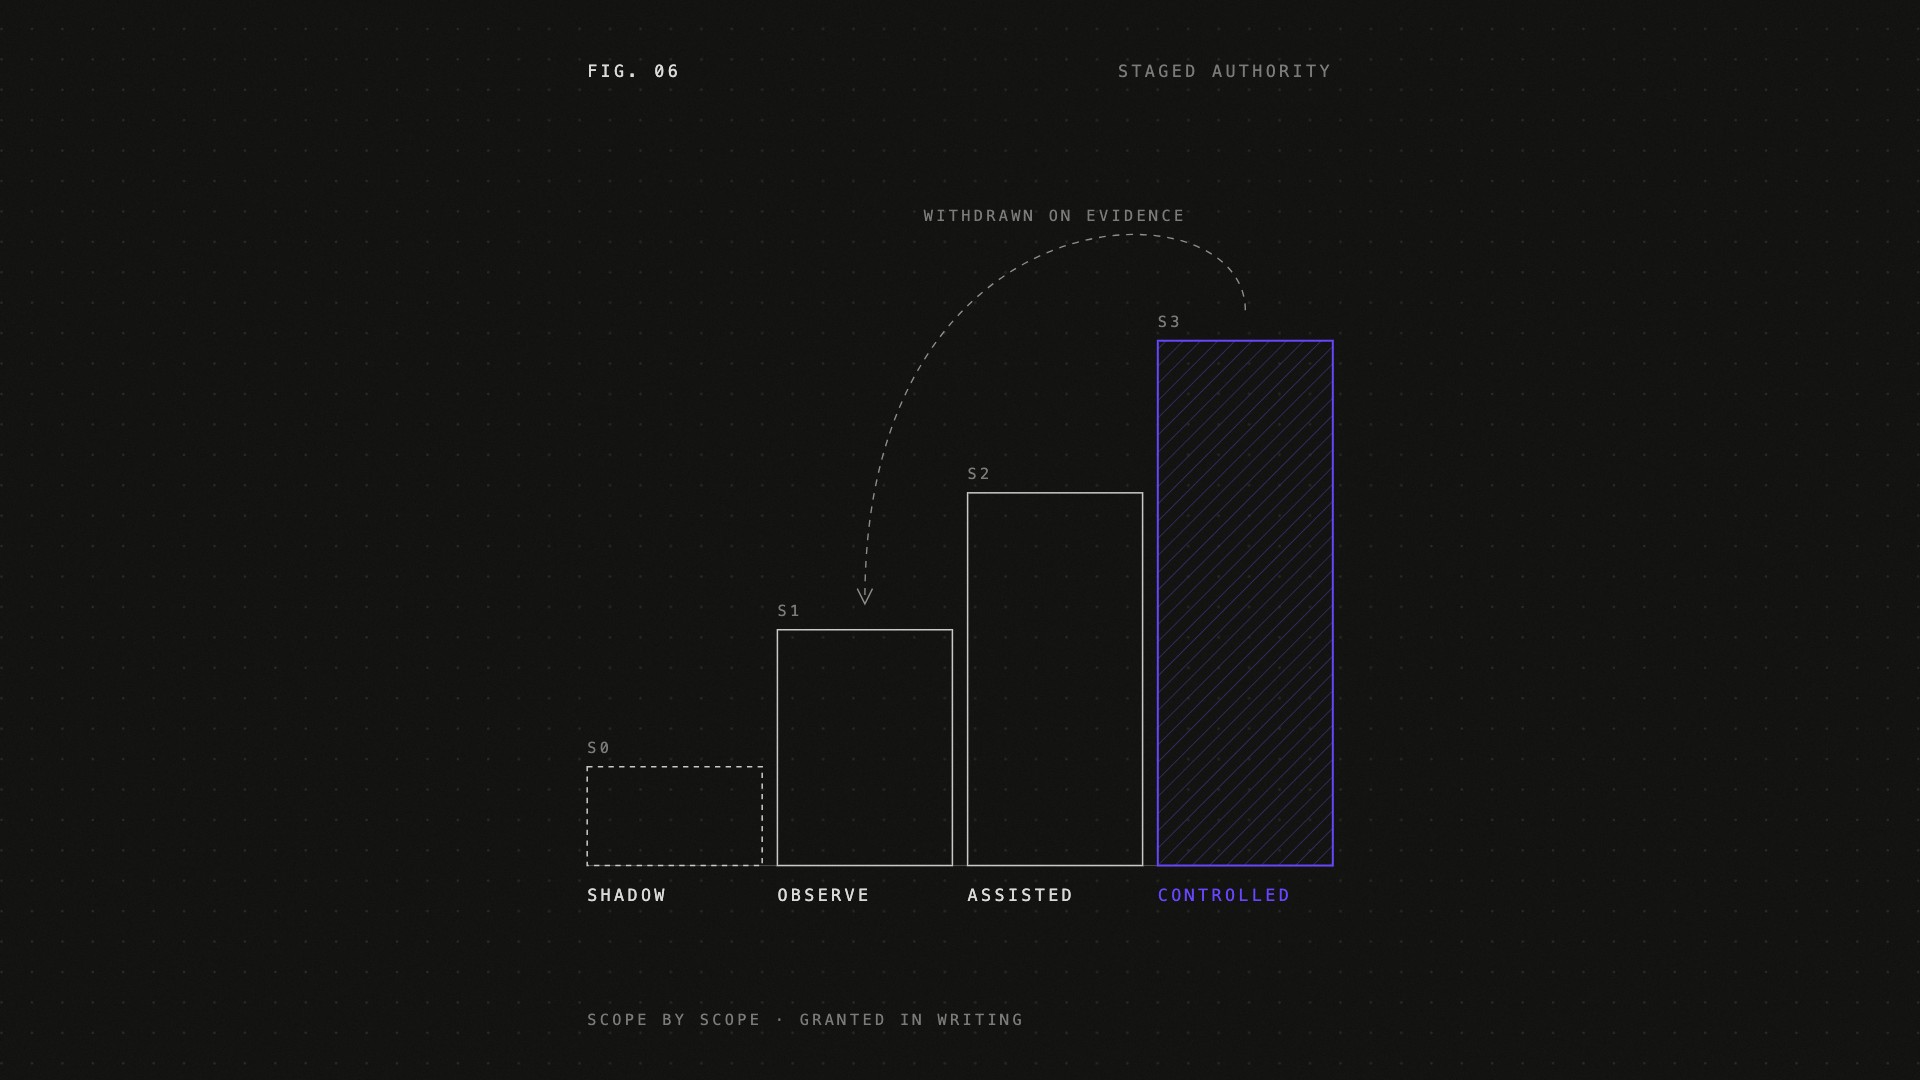
Promotion is granted per scope: a domain, an asset tier, an action class. An institution may run Controlled Autonomy on endpoint isolation and Assisted Response on identity. Nothing in this framework requires an institution to grant more than Stage 1.
Promotion
The institution's named policy owner decides promotion, in writing, as a versioned policy change subject to approval, impact assessment and logging. Glemad recommends on the evidence from the current stage and supplies the records. Promotion to Stage 3 for any scope additionally requires a Glemad Safety Review of the deployment's calibration, safety counts and evidence completeness over the shadow and assisted periods.
Withdrawal
Authority is withdrawn when the evidence changes. Triggers include failed calibration, unintended disruption from an action, degraded or missing telemetry, suspected compromise of the observation channel, a policy change that alters the risk picture, a material model update, or a human override. Reverting to a lower stage is a recorded action with a stated reason, executable by the institution at any time without Glemad's involvement.
Machine-speed deployment
Some defence must happen faster than a person can be consulted: a flood arriving at a network boundary, a compromised host beginning to encrypt. Where a Glemad system acts in microseconds, including Inline hardware in the network path, the following apply in addition to every other requirement. The action runs only under a pre-authorised protocol naming its trigger, scope and bounded worst-case impact. The protocol is evaluated at Tier E of the Model Evaluation and Red-Teaming Standard before authorisation. Hardware fails open, so that a failure of the defence never becomes a failure of the service. Every machine-speed action is reviewed afterwards with the full record, and a protocol whose review finds it acted outside its scope is suspended.
Updates to models and policy
Learning and updates run under governance. Every model update follows one path: offline validation against historical and synthetic scenarios, the safety regression suite, limited deployment with expanded monitoring, gradual expansion, and rollback on anomaly, designed so that any update can be reverted within 60 seconds. Model parameters never change through a live feedback loop; new versions are trained offline, evaluated against the frozen suite, run in shadow, calibrated, and only then promoted. Authority bounds cannot expand, hard rules are invariant, the rate of change is capped, and every parameter update is logged with before and after values, triggering signals and approval status.
Policy updates require approval, impact assessment and audit logging. Policies are versioned and integrity-monitored, so an attempt to relax a constraint or widen authority is treated as policy poisoning and refused.
Obligations of Glemad
- Establish and record the telemetry coverage each stage requires.
- Provide the records on which promotion is decided, and recommend against promotion when they do not support it.
- Communicate safety-relevant findings to affected institutions.
- Keep every deployment reversible to a lower stage by the institution alone.
- Review significant events with the institution and feed findings back under governance.
- Never expand a deployment's authority without the institution's recorded decision.
Obligations of the institution
- Maintain meaningful telemetry from protected infrastructure.
- Keep people available for high-impact decisions, policy updates and emergency override.
- Maintain policies that correctly encode security, compliance and regulatory requirements, and keep any mission dependency graph current.
- Operate a governance process for policy approval, update authorisation, incident review and accountability.
Glemad helps establish each of these.
Stewardship
Deployment is not an installation. Systems are monitored for drift and unexpected behaviour across months. Improvements from research reach production only through the update path above. Accountability for how Glemad systems are used stays with Glemad and with the people who grant them authority, for as long as the systems run.